Overview
This guide describes how to configure and use Identity Guardian on supported Zebra wearable computers, which feature a specialized layout for smaller displays.
The wearable UI is applied automatically when Identity Guardian is launched on a supported device model. The experience is designed to be consistent with the standard Identity Guardian authentication framework while being optimized for limited screen sizes.
Scope
In-Scope Features
The following features are supported for the wearable UI:
- Admin Bypass Authentication
- Barcode Authentication
- NFC Authentication
- Face Authentication
- Passcode Authentication
- Alternate Sign-In
- Switch User
- Sign Out
- Suppress Camera Preview
- Single Sign-On (SSO)
- SSO Temporary ID
- Guardian Safe
- Auto-Fill SSO Login
Out-of-Scope Features
The following features are not supported for the wearable UI:
- Personally Assigned Device mode
- User enrollment
- Managed Configuration values:
- Comparison Source: CLOUD and LEGACY BARCODE
- Primary Authentication Factor: CLOUD_PASSCODE
Supported Devices
| Device | Supported Status | Support Information |
|---|---|---|
| WS301 | Supported | Supports all authentication methods described in this document, subject to available hardware. |
| WS501 | Supported (Limited) | No built-in front camera; face authentication cannot be performed. |
Prerequisites
Confirm the following requirements for wearable devices prior to deployment:
- Identity Guardian Installation & Licensing: Identity Guardian is installed. An Identity Guardian license is required for facial biometric authentication, SSO authentication, SSO Temporary ID, and for Guardian Safe operation on supported wearable devices.
- Device Ownership: The device is deployed as a Shared Device. Personally Assigned Device mode is not supported on wearable devices.
- Android Screen Lock Configuration: The device Android screen lock is set to "None." Other screen lock types (e.g., Swipe, PIN) are incompatible.
- Pre-Enrolled User Profiles: When the Comparison Source is BARCODE or NFC, users must already be enrolled beforehand from a standard Zebra mobile computer. On-device user enrollment is not supported directly on wearable devices. The SSO-only configuration (no Comparison Source) does not use a barcode or NFC card.
- SSO Integration: If using SSO, Identity Guardian must be integrated with the organization's identity provider (IdP).
- Network Connectivity: If using Guardian Safe, internet access is required. If using SSO, the device must maintain network connection to contact the identity provider for SSO sign-in.
- User Barcodes: For Guardian Safe and Auto-Fill SSO Login, user barcodes must be generated with Identity Guardian v1.6 or later.
- Zebra DNA Cloud: For Guardian Safe, the organization must be registered with Zebra DNA Cloud, and the device must be enrolled and connected to Zebra DNA Cloud.
- DataWedge Profile Configuration: For barcode-based authentication, the Identity Guardian DataWedge profile is present and active on the device.
Configuration
To enable the wearable experience, configure Identity Guardian Managed Configurations using a supported EMM or Zebra DNA Cloud. This section covers only the parameters relevant to wearable devices.
Hardware Constraints: Since WS501 does not feature a camera, FACE must not be selected for any authentication factor. For SSO Temporary ID on WS501 devices, in SSO Authentication Configuration set Authentication Mode to PIN.
SSO-Only (No Comparison Source)
Standalone SSO operates without a physical Comparison Source, relying entirely on the IdP for user authentication.
- Usage Mode: Set Application Mode to Authentication.
- Shared Device Authentication: Set the authentication factors for each Verification Setup:
- Comparison Source: NONE
- Primary Authentication Factor: SSO
- Secondary Authentication Factor: NONE
- Fallback Authentication Method: NONE or ADMIN BYPASS PASSCODE
Multi-Factor Authentication (with a Comparison Source)
Multi-factor authentication combines a physical token (barcode or NFC card) with one or more authentication factors (such as FACE, PASSCODE, or SSO) for user authentication.
- Usage Mode: Set Application Mode to Authentication.
- Shared Device Authentication: Set the authentication factors for each Verification Setup:
- Comparison Source: BARCODE or NFC
- Primary Authentication Factor: FACE, PASSCODE, or SSO
- Secondary Authentication Factor: FACE, PASSCODE, SSO or NONE
- Fallback Authentication Method: NONE, PASSCODE, FACE, or ADMIN BYPASS PASSCODE
Note: Configuring other Comparison Source values or Authentication Factors (such as SSO, CLOUD_PASSCODE, or ANDROID_LOCK) may result in undefined behavior on wearable devices and is not supported.
Lock Screen
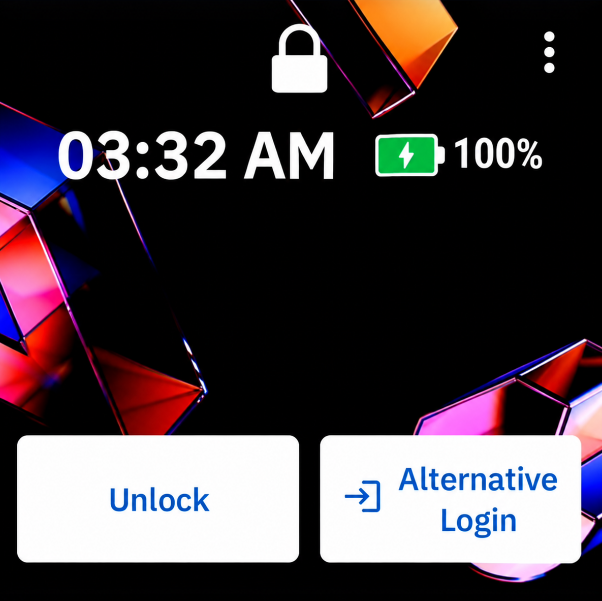
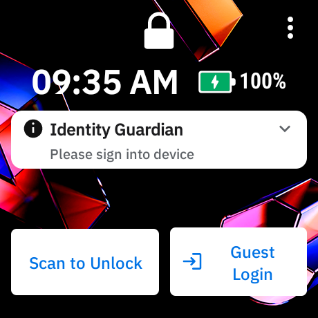
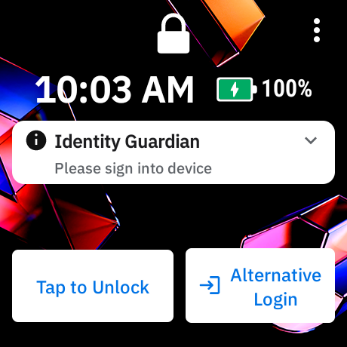
The lock screen on a wearable device displays the time, battery status, an Identity Guardian status message, and one or two action buttons. The buttons presented are determined by the managed configuration.
Lock Screen Button Configurations
The lock screen dynamically displays action buttons based on the deployed Managed Configuration. The primary (left) button initiates the primary authentication flow, while the secondary (right) button provides an alternative sign-in path or user session switch.
SSO-Only (No Comparison Source): For standalone SSO deployments, the lock screen displays a direct unlock option, since no physical token scanning is required to initiate the authentication process.
| Screen Capture | Primary (Left) Button | Secondary (Right) Button | Managed Configuration |
|---|---|---|---|
|
Unlock |
Configurable (e.g., Alternative Login) |
|
Multi-Factor Authentication (with a Comparison Source): For deployments utilizing a physical token, the lock screen prompts the operator to perform an initial scanning or tapping action to identify the user before proceeding to the configured login step.
| Screen Capture | Primary (Left) Button | Secondary (Right) Button | Managed Configuration |
|---|---|---|---|
|
Scan to Unlock |
Configurable (e.g., Guest Login) |
|
|
Tap to Unlock |
Configurable (e.g., Alternative Login) |
|
Usage
Sign In (With SSO)
The login sequence for sign-in with SSO executes according to the defined authentication factors: Comparison Source (if configured), Primary Authentication, and Secondary Authentication. SSO can function as the sole authentication factor (standalone), or the primary or secondary factor following a physical barcode scan or NFC card tap.
Scenario 1: SSO-Only Authentication
Shared Device Authentication Configuration:
- Comparison Source: None
- Primary Authentication: SSO
- Secondary Authentication: None
| Instructions | Screen Capture |
|---|---|
|
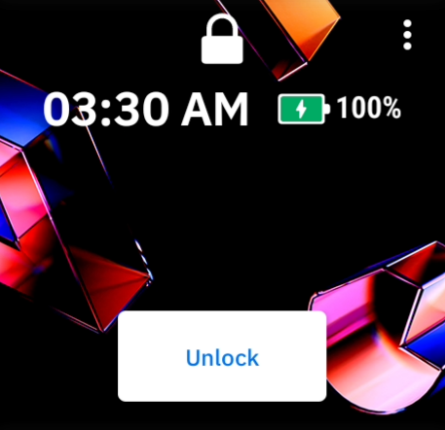
Step 1: On the lock screen, tap Unlock. |
|
|
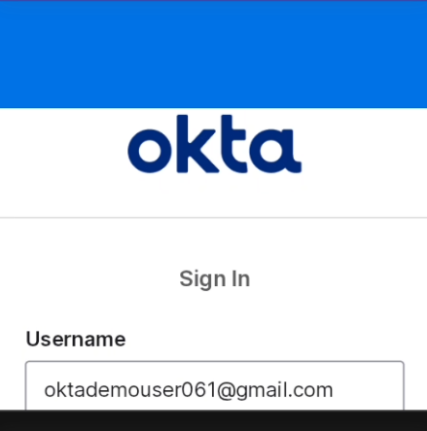
Step 2: The SSO sign-in screen appears according to the configured identity provider service (Okta in this example). Enter the user name. |
|
|
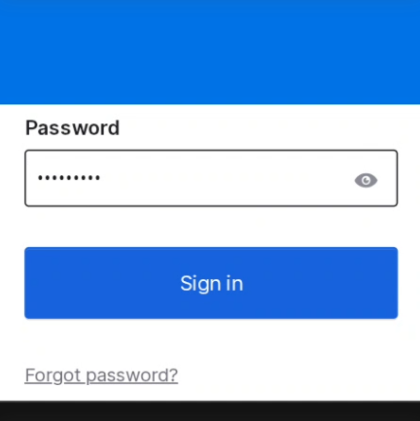
Step 3: Scroll down and enter the password, then tap Sign In. |
|
|
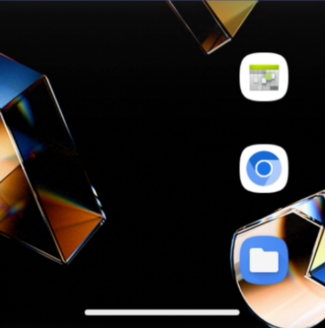
Step 4: The device unlocks and the home screen appears. |
|
Scenario 2: Barcode, Passcode, and SSO Authentication
Shared Device Authentication Configuration:
- Comparison Source: Barcode
- Primary Authentication: Passcode
- Secondary Authentication: SSO
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, scan the user barcode. |
|
|
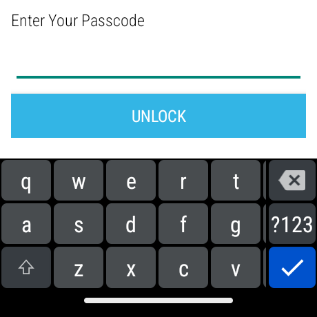
Step 2: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 3: The SSO sign-in screen appears according to the configured identity provider service (Okta in this example). Enter the user name. |
|
|
Step 4: Scroll down and enter the password, then tap Sign In. |
|
|
Step 5: The device unlocks and the home screen appears. |
|
Scenario 3: NFC and SSO Authentication
Shared Device Authentication Configuration:
- Comparison Source: NFC
- Primary Authentication: SSO
- Secondary Authentication: None
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, tap Unlock. |
|
|
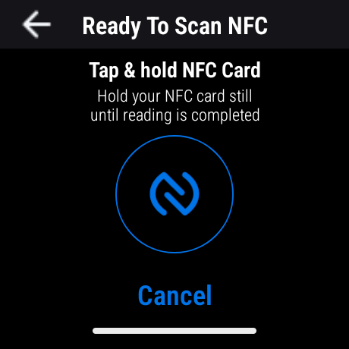
Step 2: Tap the user NFC card against the device. |
|
|
Step 3: The SSO sign-in screen appears according to the configured identity provider service (Okta in this example). Enter the user name. |
|
|
Step 4: Scroll down and enter the password, then tap Sign In. |
|
|
Step 5: The device unlocks and the home screen appears. |
|
Sign In (Without SSO)
The login sequence for sign-in without SSO executes according to the defined authentication factors: Comparison Source, Primary Authentication, and Secondary Authentication. These scenarios rely on local device credentials for authentication.
Scenario 1: Barcode, Face, and Passcode Authentication
Shared Device Authentication Configuration:
- Comparison Source: Barcode
- Primary Authentication: Face
- Secondary Authentication: Passcode
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, scan the user barcode. |
|
|
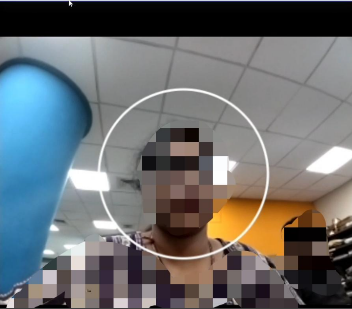
Step 2: The front camera activates for face verification. Position the face within the on-screen guide. |
|
|
Step 3: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 4: The device unlocks and the home screen appears. |
|
Scenario 2: NFC, Face, and Passcode Authentication
Shared Device Authentication Configuration:
- Comparison Source: NFC
- Primary Authentication: Face
- Secondary Authentication: Passcode
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, select Tap to Unlock. |
|
|
Step 2: Tap the user NFC card against the device. |
|
|
Step 3: The front camera activates for face verification. Position the face within the on-screen guide. |
|
|
Step 4: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 5: The device unlocks and the home screen appears. |
|
Scenario 3: Barcode, Passcode, and Face Authentication with Suppress Camera Preview
Shared Device Authentication Configuration:
- Comparison Source: Barcode
- Primary Authentication: Passcode
- Secondary Authentication: Face
Facial Authentication Configuration:
- Suppress Camera View: On
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, scan the user barcode. |
|
|
Step 2: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
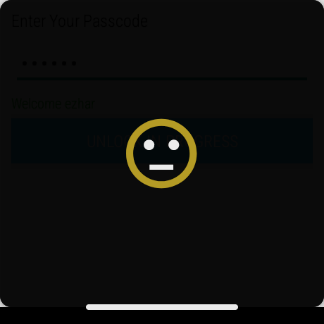
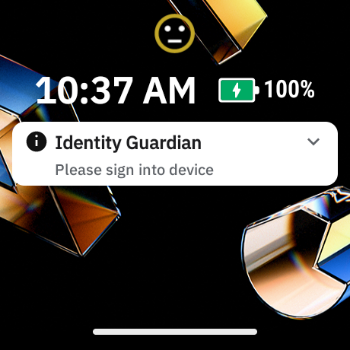
Step 3: The front camera activates for face verification. Instead of the preview screen, a yellow neutral face icon is displayed. |
|
|
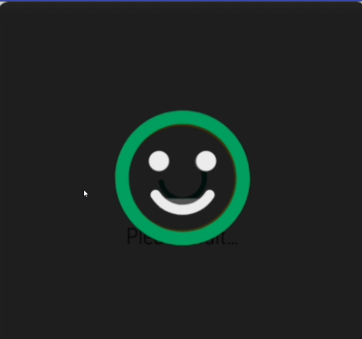
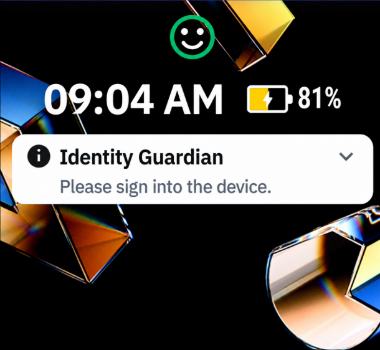
Step 4: When the face capture is acceptable, a green smiley face icon is displayed. |
|
|
Step 5: The device unlocks and the home screen appears. |
|
Scenario 4: Barcode, Face, and Passcode Authentication with Suppress Camera Preview
Shared Device Authentication Configuration:
- Comparison Source: Barcode
- Primary Authentication: Face
- Secondary Authentication: Passcode
Facial Authentication Configuration:
- Suppress Camera View: On
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, scan the user barcode. |
|
|
Step 2: The front camera activates for face verification. Instead of the preview screen, the lock screen remains with a yellow neutral face icon displayed. Capture the face. |
|
|
Step 3: When the face capture is acceptable, the icon turns into a green smiley face. |
|
|
Step 4: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 5: The device unlocks and the home screen appears. |
|
Scenario 5: NFC, Passcode, and Face Authentication with Suppress Camera Preview
Shared Device Authentication Configuration:
- Comparison Source: NFC
- Primary Authentication: Passcode
- Secondary Authentication: Face
Facial Authentication Configuration:
- Suppress Camera View: On
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, select Tap to Unlock. |
|
|
Step 2: Tap the user NFC card against the device. |
|
|
Step 3: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 4: The front camera activates for face verification. Instead of the preview screen, a yellow neutral face icon is displayed. Capture the user's face. |
|
|
Step 5: When the face capture is acceptable, the icon turns into a green smiley face. |
|
|
Step 6: The device unlocks and the home screen appears. |
|
SSO Temporary ID
SSO Temporary ID enables sign-in with SSO credentials at the start of a shift, followed by a short PIN for subsequent sign-ins during the shift, eliminating the need to re-enter SSO credentials or use a barcode or NFC card. The Temporary ID clears automatically when the user signs out. For more details, see SSO Temporary ID in the user guide.
Configuration
Configure the Identity Guardian Managed Configurations below using a supported EMM or Zebra DNA Cloud.
Shared Device Authentication: Set the authentication factors for each Verification Setup:
- Comparison Source: NONE
- Primary Authentication Factor: SSO
- Secondary Authentication Factor: NONE
SSO Authentication Configuration: Configure the following settings:
- TempID: true
- Authentication Mode: PIN, FACE, or ANY (Note: FACE and ANY do not apply to WS501 due to the lack of a front-facing camera).
- Temp Id Type: Numeric or AlphaNumeric
- Minimum Length: 4 to 20 (default: 4)
- Minimum Uppercase Letters: 0 or 1 (Set if Temp Id Type is Alphanumeric.)
- Minimum Lowercase Letters: 0 or 1 (Set if Temp Id Type is Alphanumeric.)
- Minimum Numbers: 0 or 1 (Set if Temp Id Type is Alphanumeric.)
- Minimum Special Symbols: 0 or 1 (Set if Temp Id Type is Alphanumeric.)
First-Time Sign-In
The first SSO sign-in on the device offers the user to create a Temporary ID.
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, tap Unlock. |
|
|
Step 2: The SSO sign-in screen appears according to the configured identity provider service (Okta in this example). Enter the user name. |
|
|
Step 3: Scroll down and enter the password, then tap Sign In. |
|
|
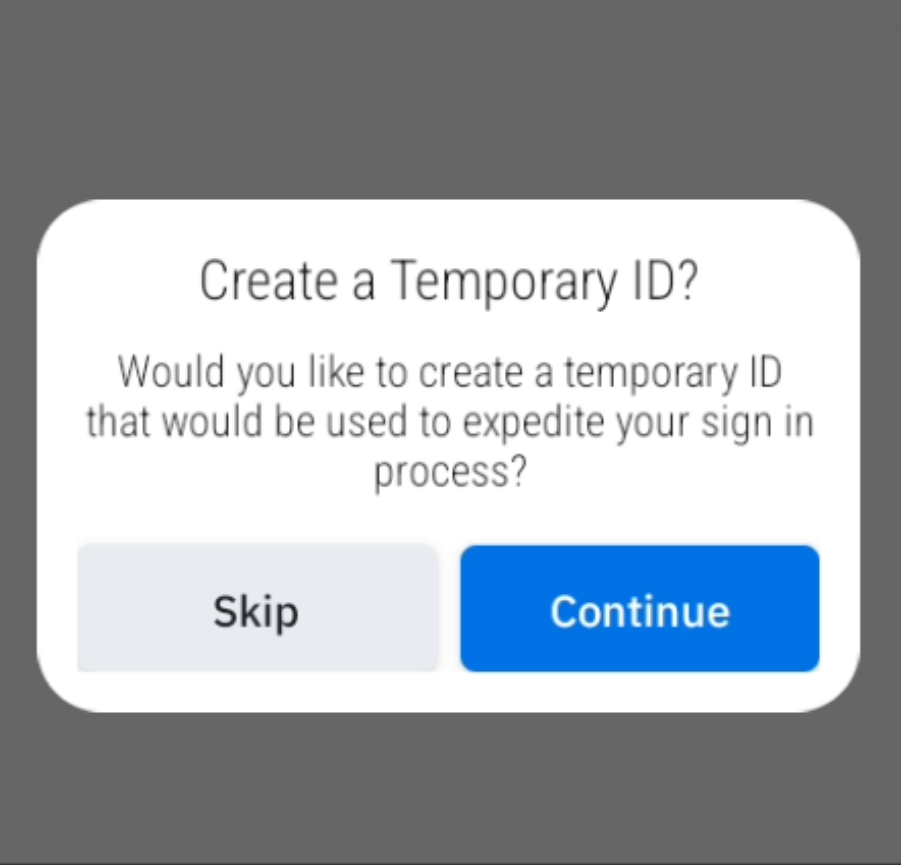
Step 4: The prompt appears to create a Temporary ID. Tap Continue. |
|
|
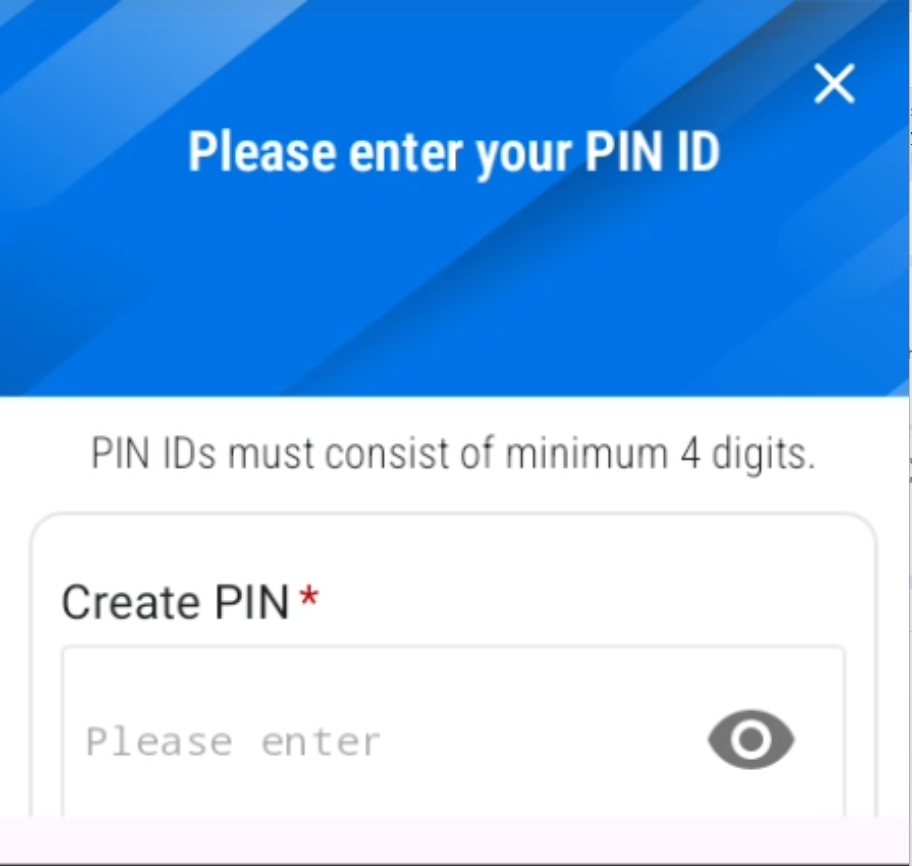
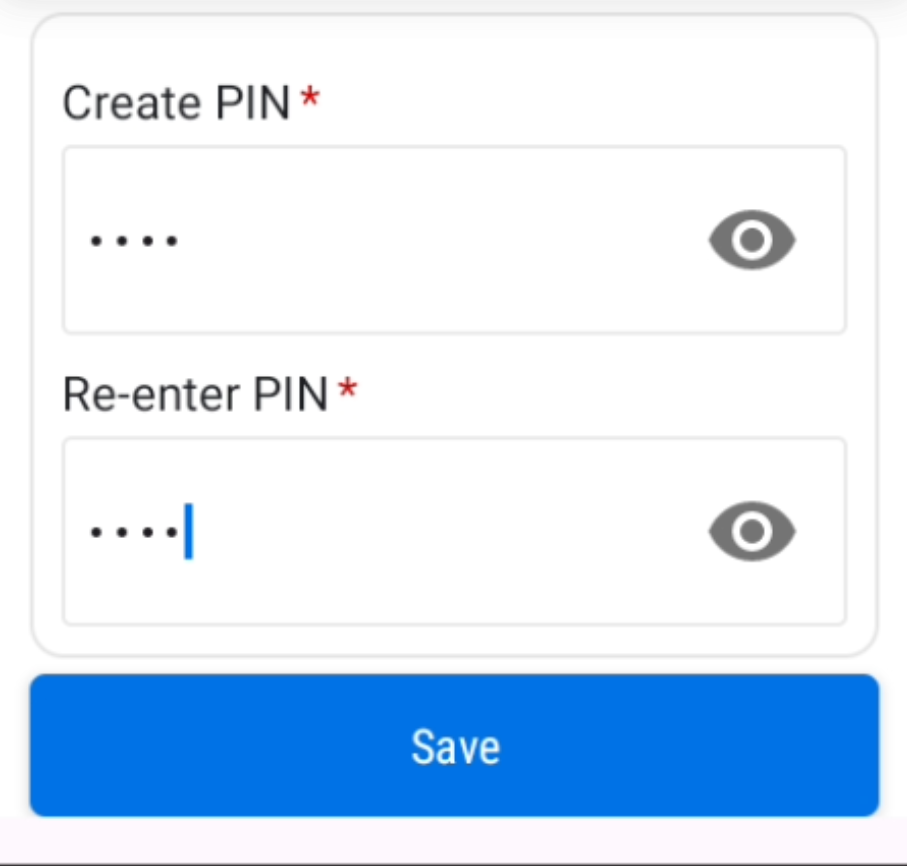
Step 5: Enter a PIN to create; it must meet the requirements (e.g., minimum of 4 digits). |
|
|
Step 6: Confirm the PIN entry and tap Save. |
|
|
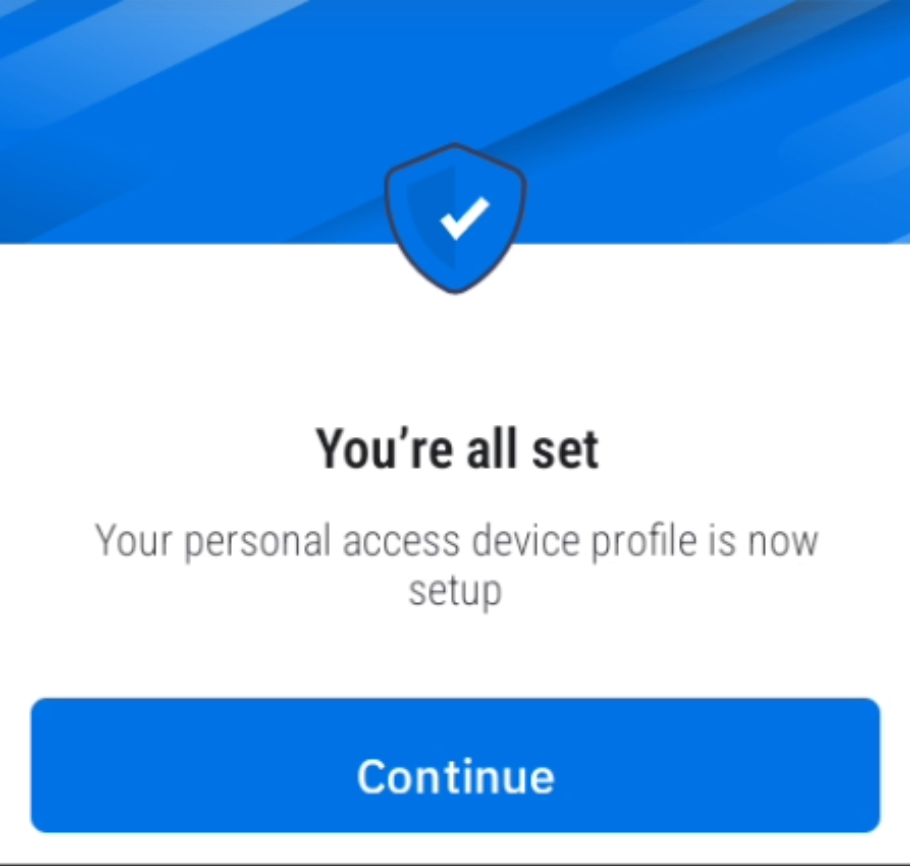
Step 7: The profile setup is complete. Tap Continue. |
|
|
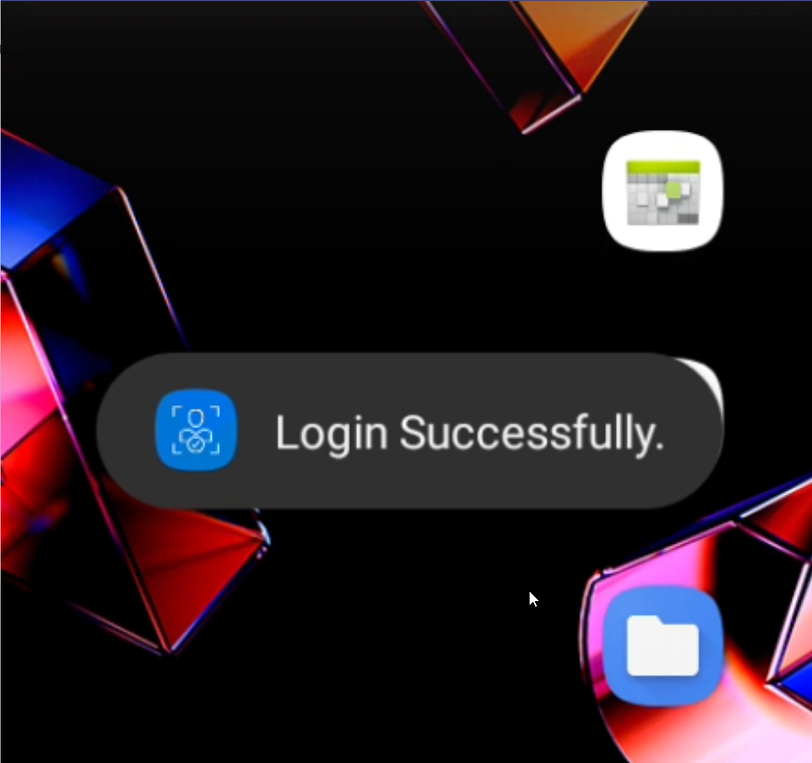
Step 8: The device unlocks. The user logs in successfully. |
|
|
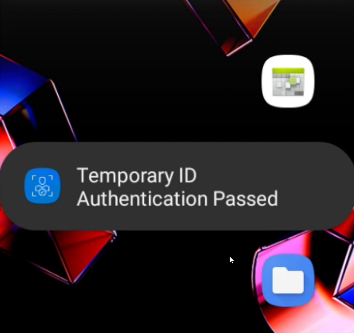
Step 9: A message displays indicating the Temporary ID Authentication passed. |
|
Sign In with a Temporary ID
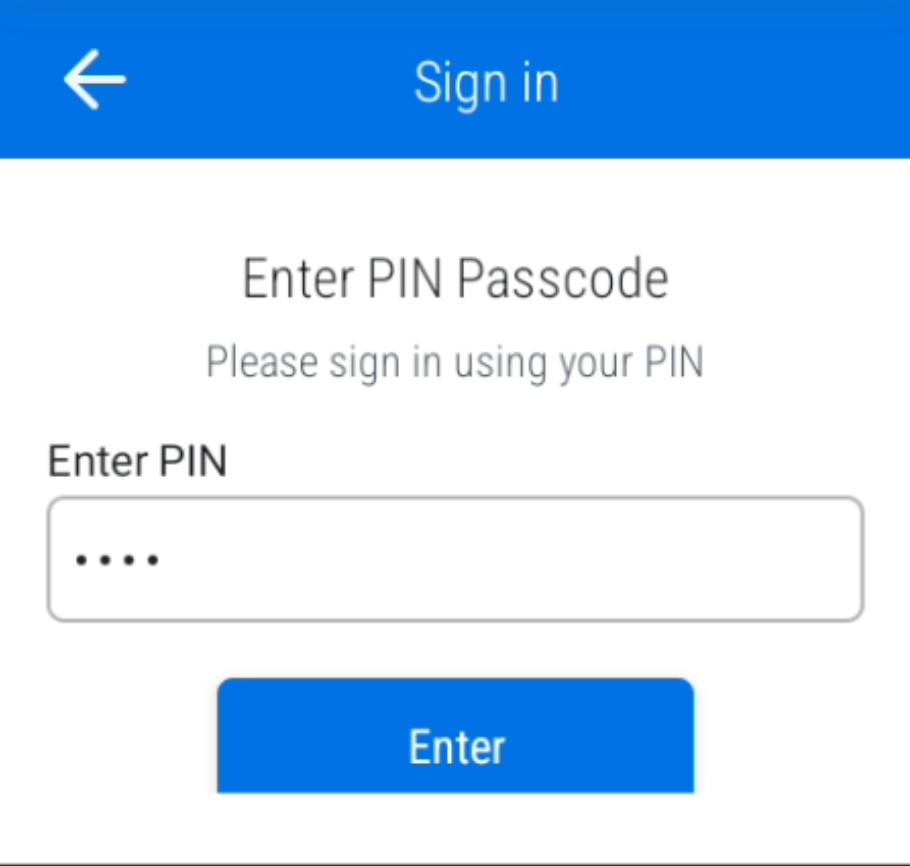
After a Temporary ID is created, subsequent sign-ins on the same device use the PIN instead of SSO credentials until the user signs out.
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, tap Unlock. |
|
|
Step 2: Enter the PIN previously created, then tap Enter. |
|
|
Step 3: The device unlocks. The user logs in successfully. |
|
|
Step 4: A message displays indicating the Temporary ID Authentication passed. |
|
Manage the Temporary ID
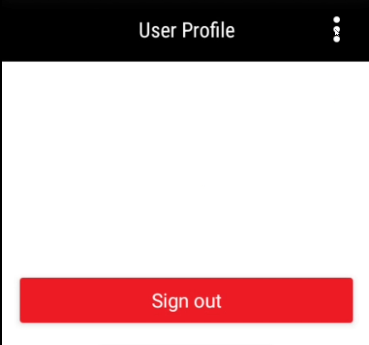
Users can view, change, or delete their Temporary ID from their Identity Guardian user profile.
View Temporary ID Status
| Instructions | Screen Capture |
|---|---|
|
Step 1: Open Identity Guardian. |
|
|
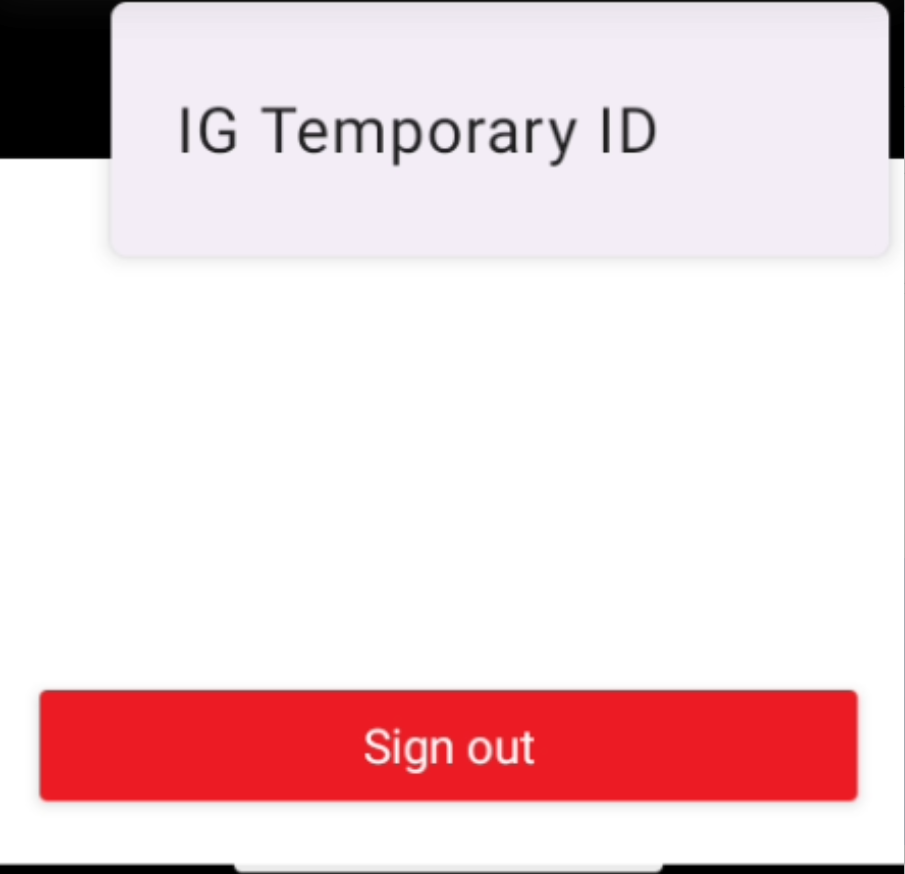
Step 2: Tap the top right menu and select IG Temporary ID. |
|
|
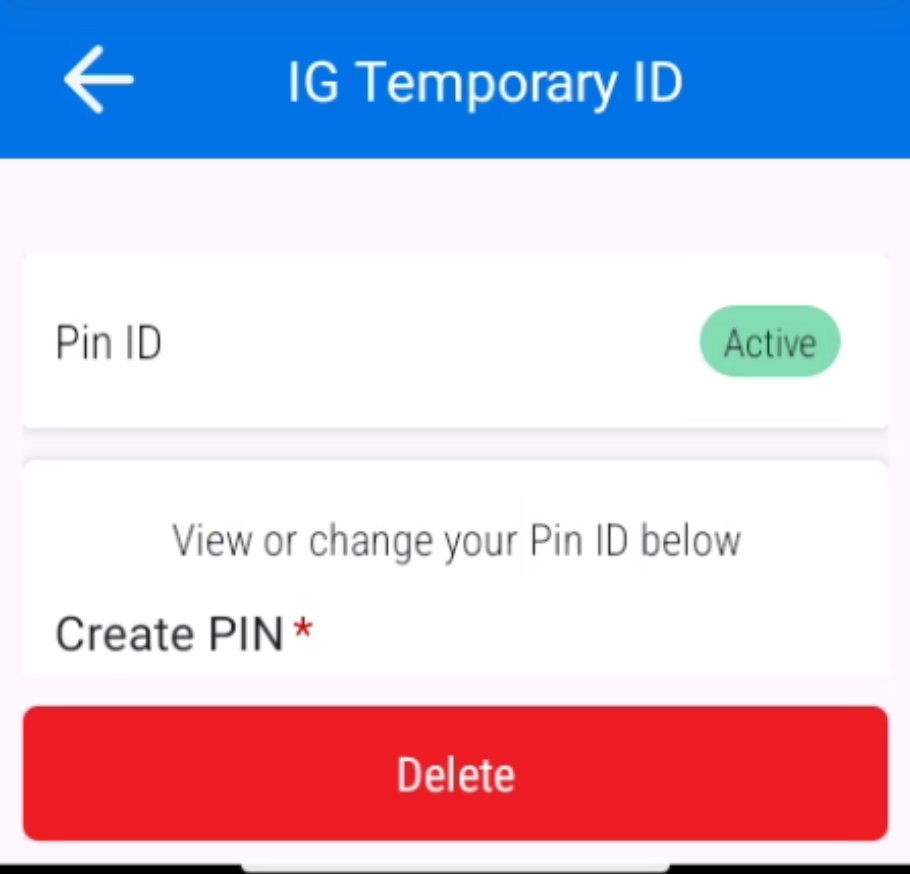
Step 3: The Pin ID status is displayed. Active indicates that a PIN is set. |
|
Change the PIN
| Instructions | Screen Capture |
|---|---|
|
Step 1: Open Identity Guardian. |
|
|
Step 2: Tap the top right menu and select IG Temporary ID. |
|
|
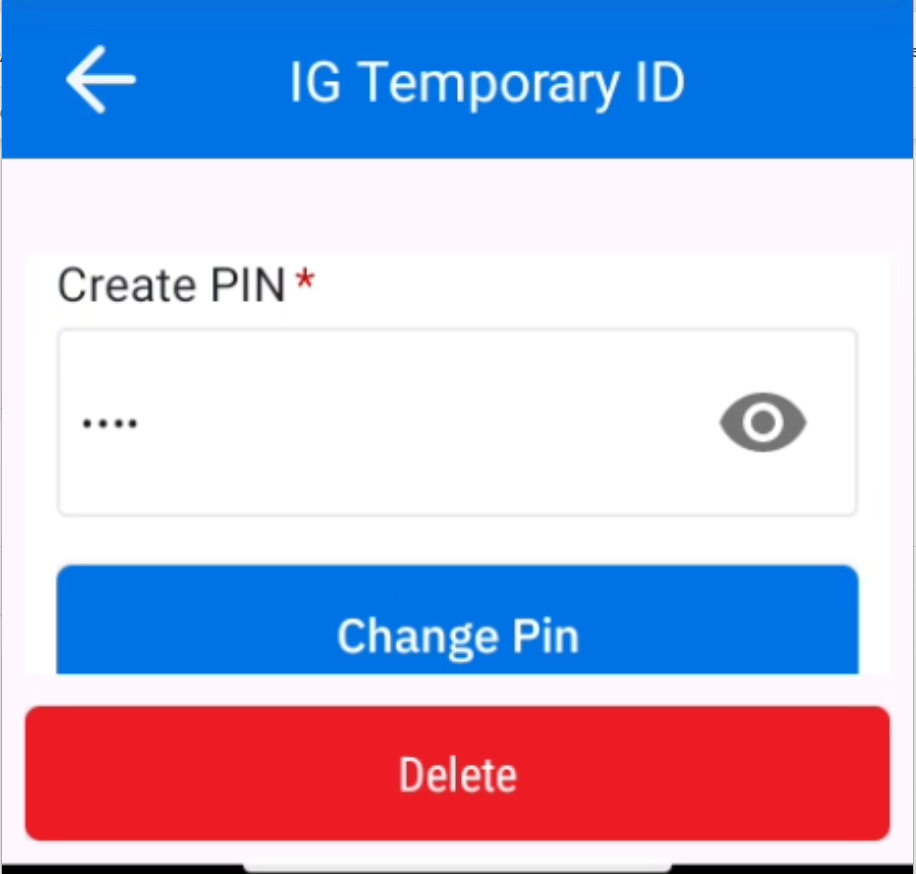
Step 3: Enter the existing PIN in the Create PIN field and tap Change PIN. |
|
|
Step 4: Scroll down and enter the new PIN. |
|
|
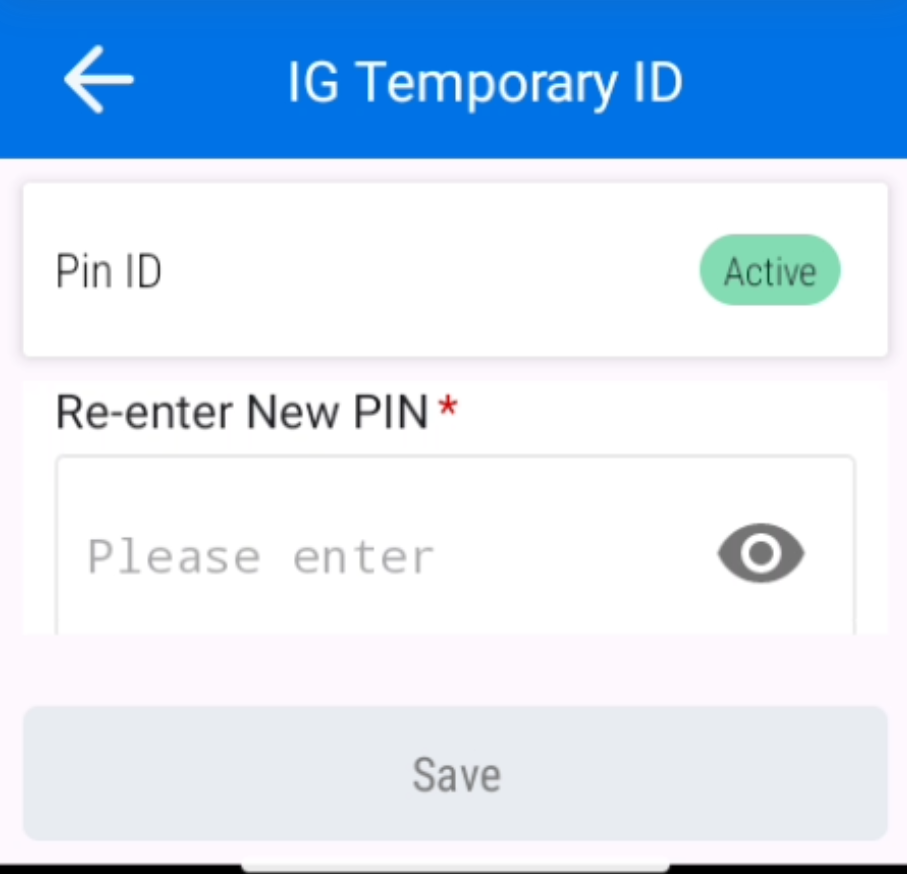
Step 5: Re-enter the new PIN. |
|
|
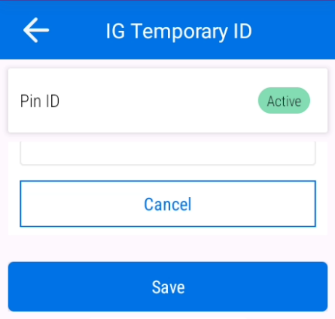
Step 6: Tap Save to replace the existing PIN with the new PIN. Or, tap Cancel to retain the existing PIN. |
|
Delete the PIN
| Instructions | Screen Capture |
|---|---|
|
Step 1: Open Identity Guardian. |
|
|
Step 2: Tap the top right menu and select IG Temporary ID. |
|
|
Step 3: Tap Delete. |
|
|
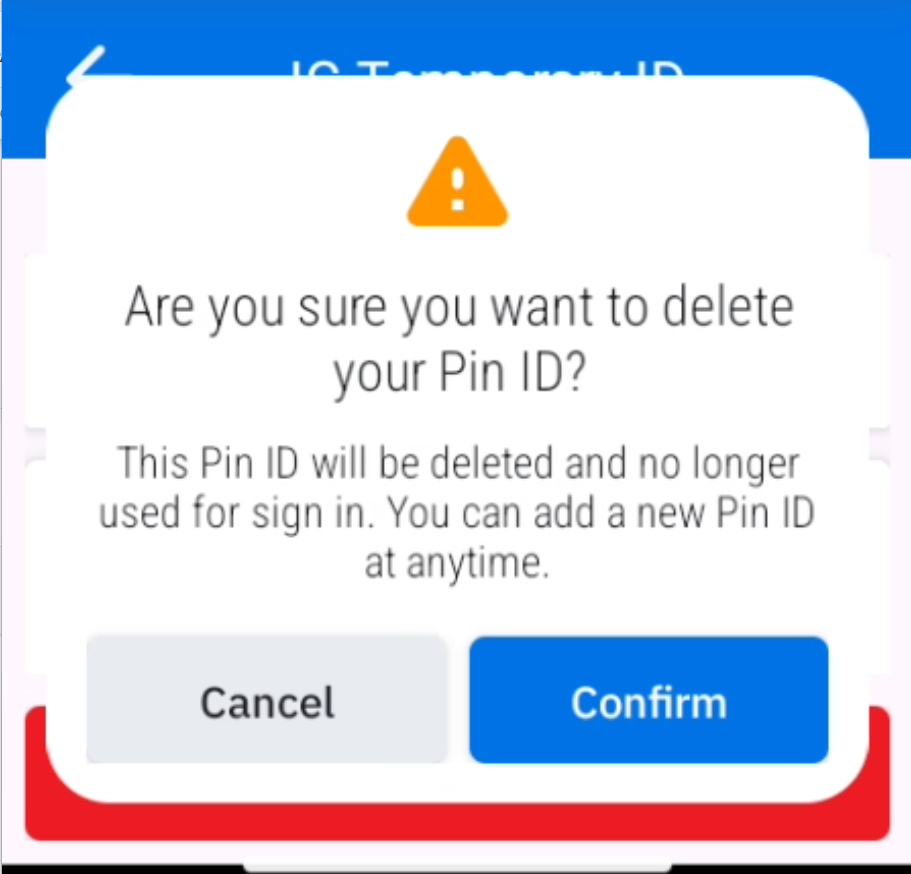
Step 4: Tap Confirm to remove the PIN ID. Or, tap Cancel to keep it. |
|
|
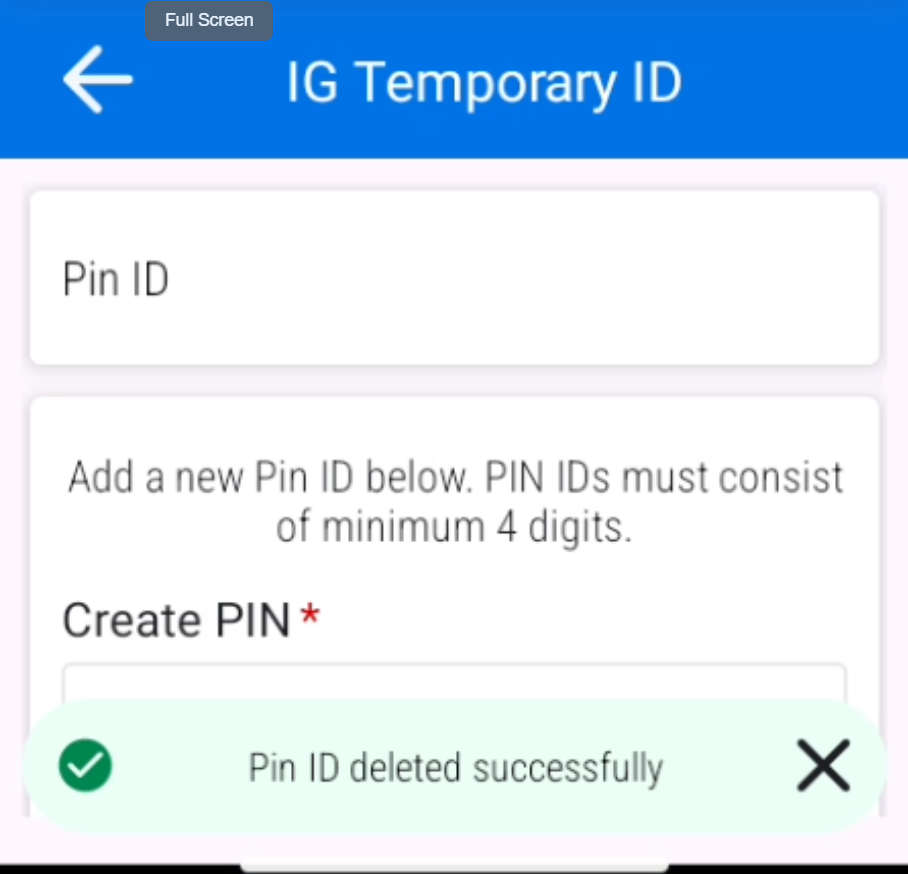
Step 5: The PIN is removed successfully and the PIN ID status disappears (previously shown as "Active"). An option appears to create a new PIN. |
|
Admin Bypass Login
Bypass the user login with the defined ADMIN BYPASS PASSCODE configured by the administrator. This applies when the Fallback Authentication Method in Shared Device Authentication is set to ADMIN BYPASS PASSCODE.
| Instructions | Screen Capture |
|---|---|
|
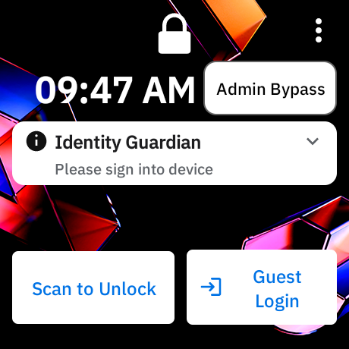
Step 1: On the lock screen, open the three-dot menu and select Admin Bypass. |
|
|
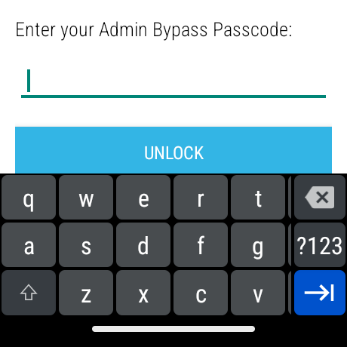
Step 2: Enter the administrator bypass passcode and select UNLOCK. |
|
|
Step 3: The device unlocks and the home screen appears. |
|
Alternate Sign-In
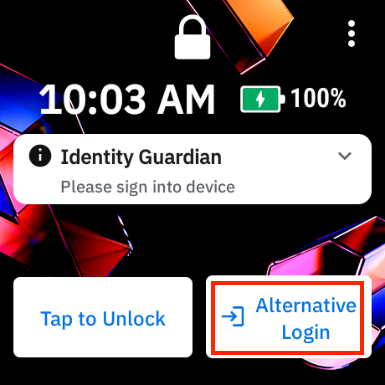
Alternate Sign-In (also known as Alternative Login) enables temporary users without permanent credentials to securely access Shared Devices while maintaining user accountability.
The button label displayed on the lock screen and the resulting authentication workflow are defined by the administrator. For configuration and workflow details, see Alternate Sign-In.
Guardian Safe
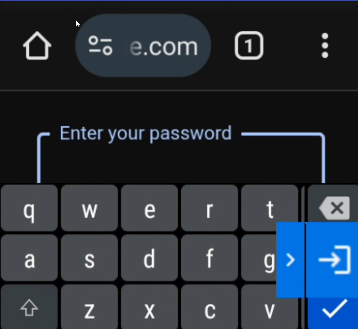
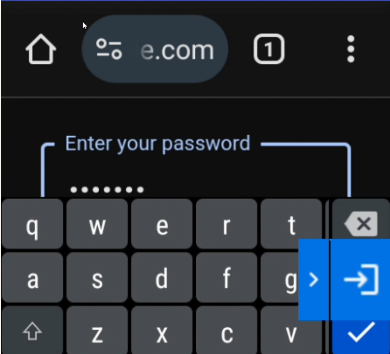
Guardian Safe securely stores a user's app credentials after a single entry and fills them in automatically on later logins, for both native apps and web apps. When Guardian Safe is active, the Guardian Safe floating button appears on app login screens where a password field is detected. For the full feature description, see Guardian Safe in the User Guide.
Prerequisites
- ZDNA Cloud Registration - Register with Zebra.com based on the instructions provided in ZDNA Cloud Setup.
- Device Enrollment - Ensure the device is enrolled and connected to Zebra DNA Cloud.
- User Barcode: Generated with Identity Guardian v1.6 or later.
- Enable Guardian Safe: Follow instructions to enable Guardian Safe and grant Accessibility Service permission.
- Shared Device Authentication Managed Configuration: Specify the following:
- User Verification Method:
- Comparison Source: Barcode or NFC
- Primary Authentication Factor: FACE or PASSCODE
- Authentication Data Storage:
- Store Authentication Data: true
- User Verification Method:
Save Credentials
| Instructions | Screen Capture |
|---|---|
|
Step 1: Open an app with a login screen (containing a user ID and password field). Tap the password field. |
|
|
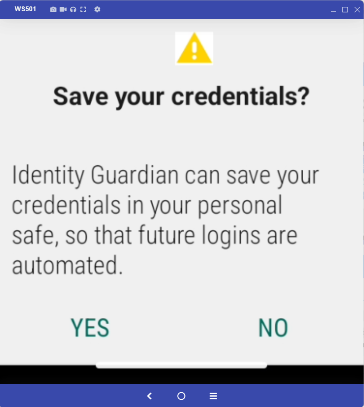
Step 2: A prompt asks whether to save the credentials. Tap Yes. If No is selected, the app is added to the Ignored Apps list. |
|
|
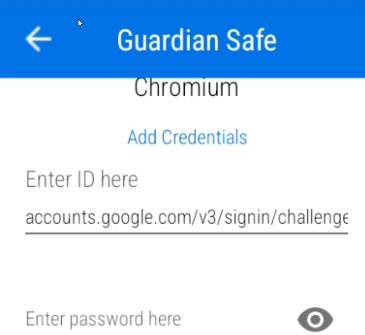
Step 3: In the Guardian Safe screen, enter the credentials. |
|
|
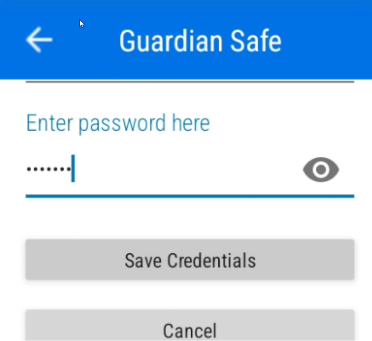
Step 4: Tap Safe Credentials. |
|
|
Step 5: The application login screen appears with the credentials auto-populated. Subsequent login attempts to the app will automatically populate the credentials. |
|
Auto-Populate Credentials
Once credentials are saved in Guardian Safe for an application, subsequent attempts to launch the app result in the credentials auto-populating.
| Instructions | Screen Capture |
|---|---|
|
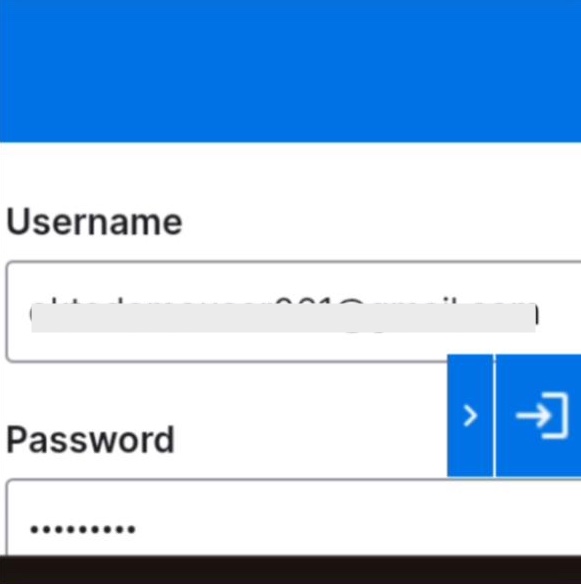
When opening an app with credentials saved in Guardian Safe, a blue Guardian Safe floating sign-in icon appears and the username and password fields auto-populate. If the fields do not populate automatically, tap the input field to trigger the action. Tap the sign-in button to proceed. |
|
Manage Saved Credentials
| Instructions | Screen Capture |
|---|---|
|
Step 1: Open Identity Guardian. |
|
|
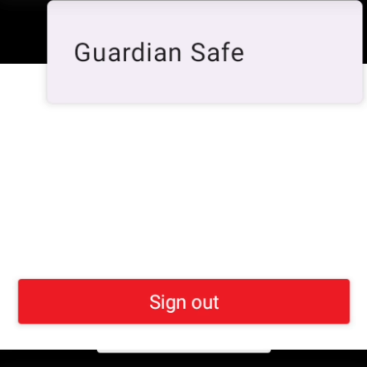
Step 2: Tap the top right menu and select Guardian Safe. |
|
|
Step 3: The Pin ID status is displayed. Active indicates that a PIN is set. |
|
Unlock Device
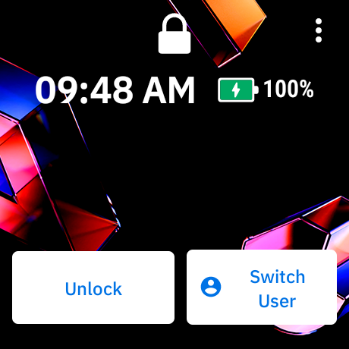
After an initial login, the user session remains active even when the screen locks due to an inactivity timeout, manual screen off, or power state change. In this state, the lock screen displays the Unlock button, allowing the signed-in user to resume the active session.
If no active session exists, the device displays the standard initial sign-in prompts (Scan to Unlock or Tap to Unlock) rather than the Unlock button.
The unlock sequence bypasses the initial identity comparison source and prompts directly for the configured authentication factors: Primary Authentication and Secondary Authentication (if enabled). Sample unlock procedures are detailed below.
Scenario 1: Face and Passcode Authentication without Suppress Camera Preview
Shared Device Authentication Configuration:
- Primary Authentication: Face
- Secondary Authentication: Passcode
Facial Authentication Configuration:
- Suppress Camera View: Off
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, tap Unlock. |
|
|
Step 2: The front camera activates for face verification. Position the face within the on-screen guide. |
|
|
Step 3: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 4: The device unlocks and the home screen appears. |
|
Scenario 2: Face and Passcode Authentication with Suppress Camera Preview
Shared Device Authentication Configuration:
- Primary Authentication: Face
- Secondary Authentication: Passcode
Facial Authentication Configuration:
- Suppress Camera View: On
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, tap Unlock. |
|
|
Step 2: The front camera activates for face verification. Instead of the preview screen, the lock screen remains with a yellow neutral face icon displayed. Capture the face. |
|
|
Step 3: When the face capture is acceptable, the icon turns into a green smiley face. |
|
|
Step 4: The passcode entry screen appears. Enter the passcode and tap UNLOCK. |
|
|
Step 5: The device unlocks and the home screen appears. |
|
View Device Information
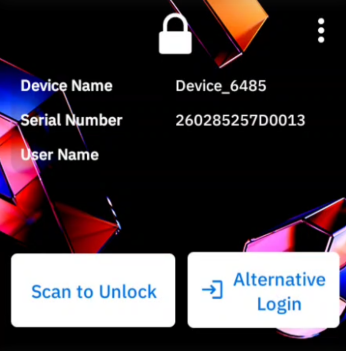
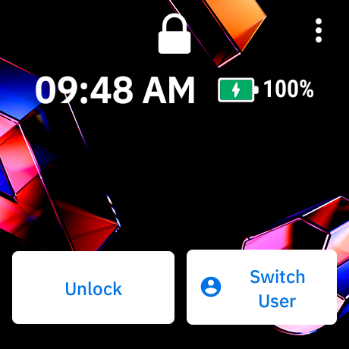
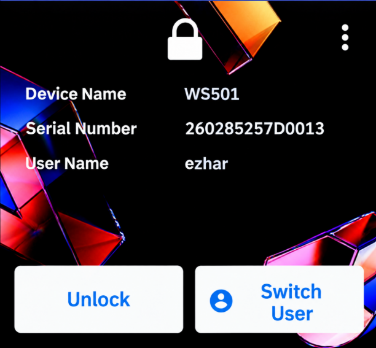
Device information, including the device name, serial number, and currently signed-in user name, can be viewed directly from the lock screen without unlocking the device. The screen UI varies depending on whether there is a user logged in.
No User Logged In: Displays the device friendly name, serial number, and indicates no active user session.
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, perform a vertical swipe up. |
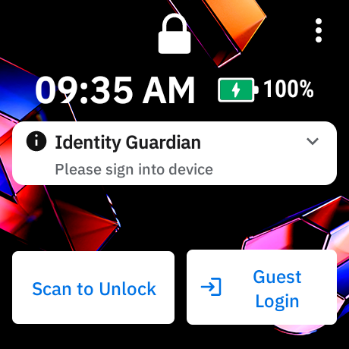
|
|
Step 2: The device friendly name and serial number are displayed. Swipe down to return to the lock screen. |
|
User Logged In: Displays the device friendly name, serial number, and the full name of the currently signed-in user.
| Instructions | Screen Capture |
|---|---|
|
Step 1: On the lock screen, perform a vertical swipe. |
|
|
Step 2: The device friendly name and serial number are displayed. |
|
Switch User
The Switch User option displays on the lock screen when a user session is active on a Shared Device. This feature enables a different user to authenticate and begin a new session without requiring the previous user to explicitly sign out beforehand.
On a locked device with an active session, the lock screen provides two primary actions:
Unlock: Prompts for the configured secondary factor or unlock sequence to resume the existing session for the currently signed-in user.
Switch User: Terminates the active session and returns the device to the initial sign-in screen (Scan to Unlock or Tap to Unlock), allowing a new user to authenticate.
Sign Out
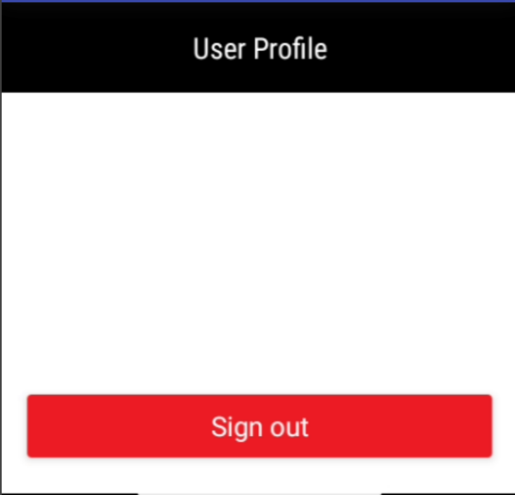
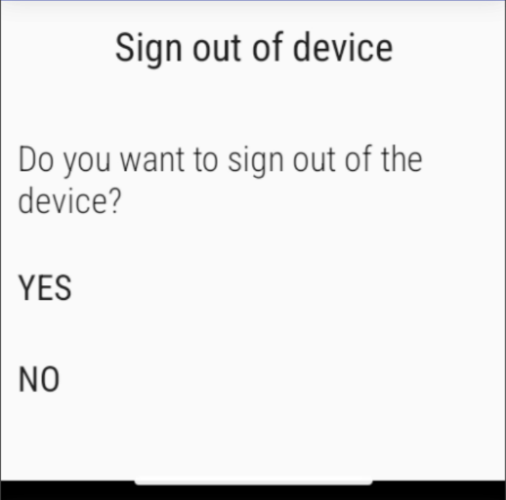
A user can sign out from the Identity Guardian user profile screen.
| Instructions | Screen Capture |
|---|---|
|
Step 1: Open Identity Guardian. |
|
|
Step 2: Tap Yes to confirm sign-out. |
|